INFORMATION SECURITY POLICY
Information Security Policy
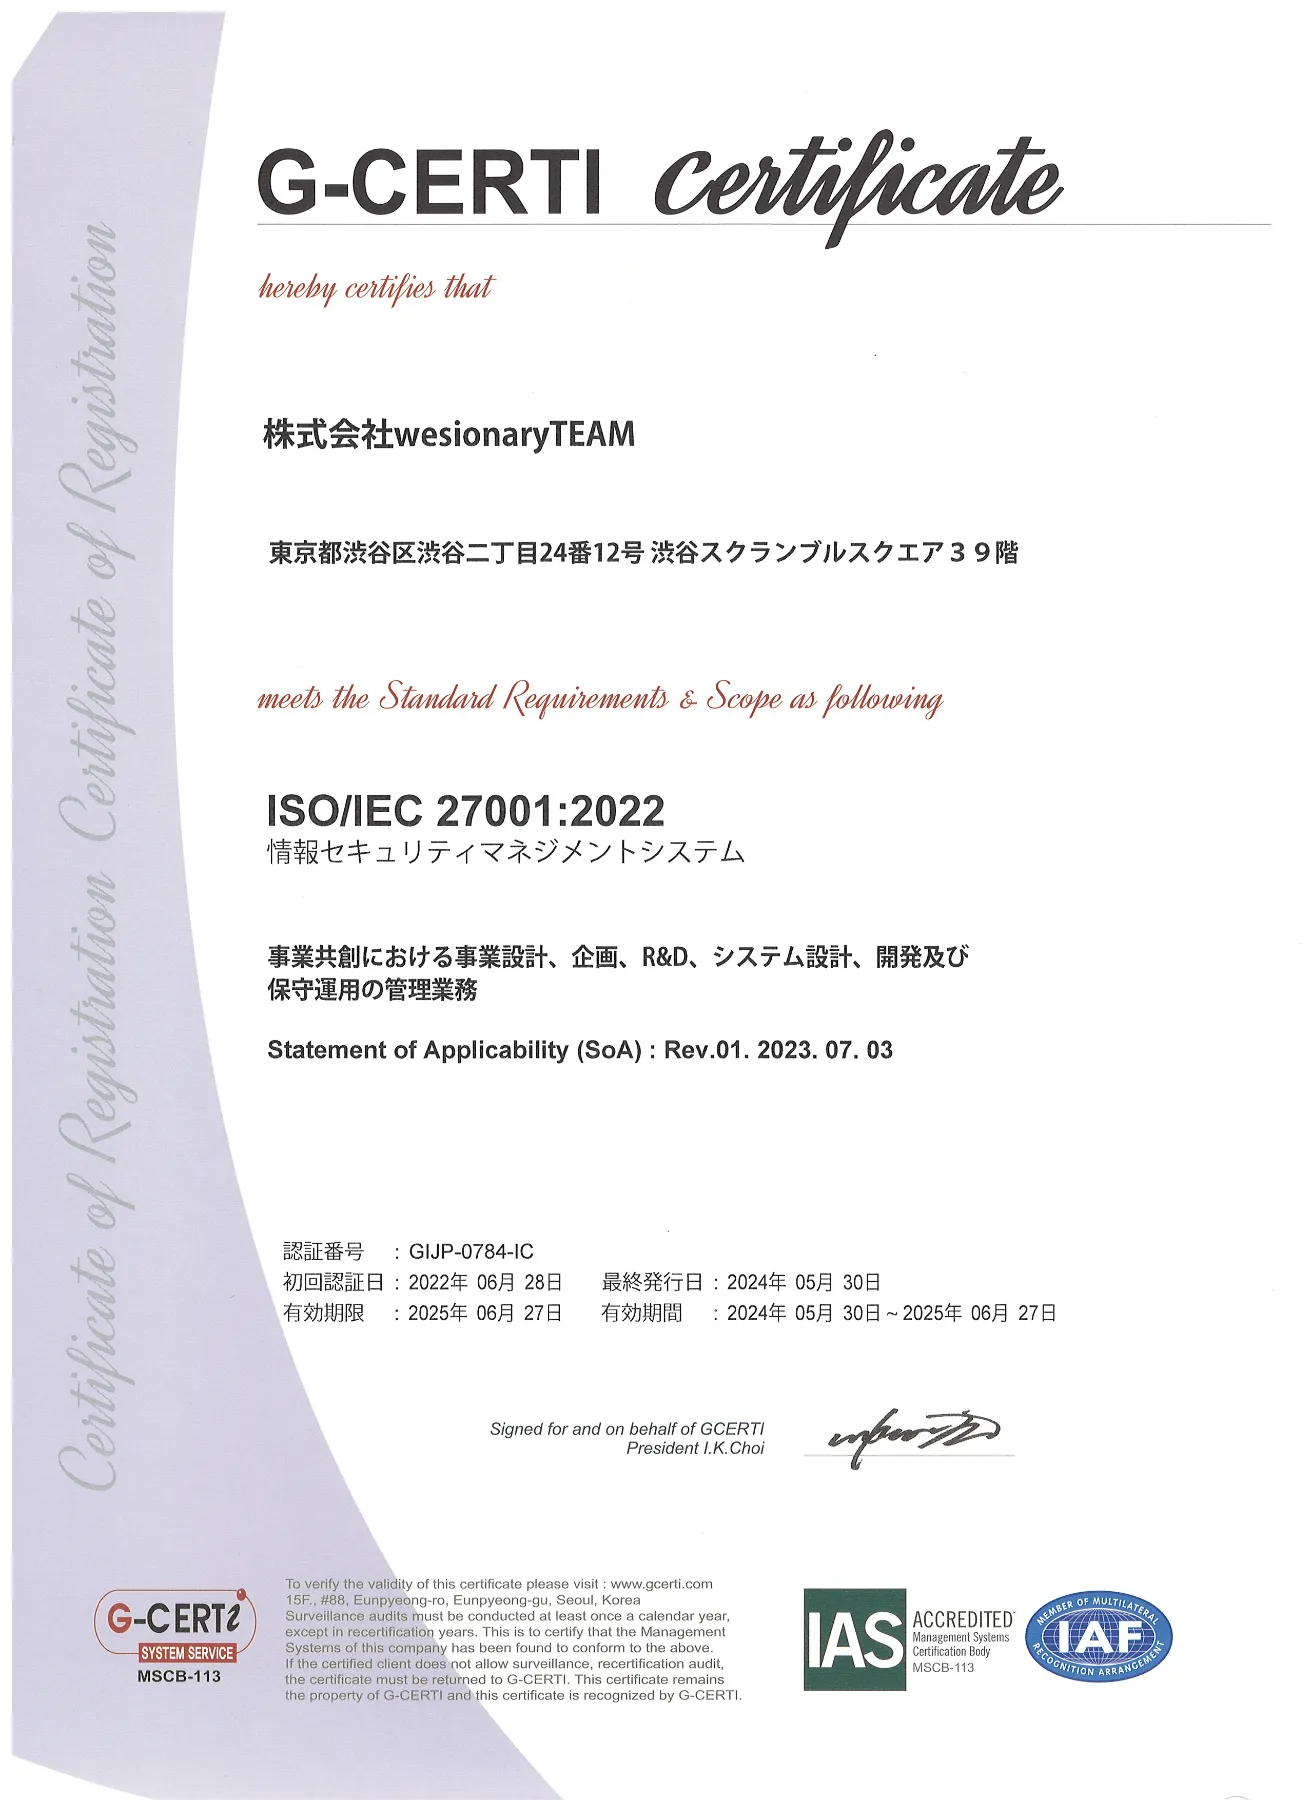
ISMS (Information Security Management System) Certified
Our vision is “Toward a society where co-creation is the norm.” We aim to realize a future in which all companies and individuals effectively combine their knowledge and resources to maximize that value.
We recognize that ensuring information security is an important management issue, and we consider it essential to protect the customer information collected through our business, as well as the information assets we handle, by taking appropriate security measures.
Through the establishment and operations of an information security management system, we aim to protect the confidentiality, integrity, and availability of the various information assets we handle in the course of our business, and to prevent security incidents such as information leaks and tampering.
To this end, we shall establish the following action guidelines for information security.
To reliably protect the confidentiality, integrity, and availability of our information assets, we take appropriate organizational and technical measures and respond to changing information technology and new threats.
To establish and continually improve our information security management system, we identify information asset risks using defined procedures and implement appropriate risk treatment.
We clearly define roles and responsibilities for information security and manage our information assets appropriately.
To ensure that everyone is aware of their responsibility for maintaining information security, we provide education and awareness activities to management, employees, and all related parties.
In the unlikely event that an information security problem occurs, we will immediately investigate the cause, keep the damage to a minimum, and strive to ensure business continuity.
With regard to information assets and their handling, we comply with laws and regulations, other social norms, and contracts with our customers.
wesionaryTEAM Co. Ltd.
Ichiro Nagata, Representative Director
First Edition: Established February 3, 2020
Second Edition: Revised March 1, 2022
Certification Obtained
ISMS (Information Security Management System)
ISO/IEC 27001:2022
Scope: Head Office
Date Obtained: June 28, 2022
Certification Number: GIJP-0784-IC